Persistent Botnet Infrastructure: Validating Containment Against Extreme Scale 

Persistent Botnet Infrastructure: Validating Containment Against Extreme Scale  TL;DR  Botnets are no longer limited to simple distributed denial-of-service campaigns. Modern botnet ecosystems operate as resilient, adaptive, and globally distributed infrastructures capable of supporting cybercrime, espionage, fraud, credential theft, ransomware delivery, and large-scale disruption. The challenge for modern enterprises is no longer simply detecting botnet activity. The real challenge is validating whether
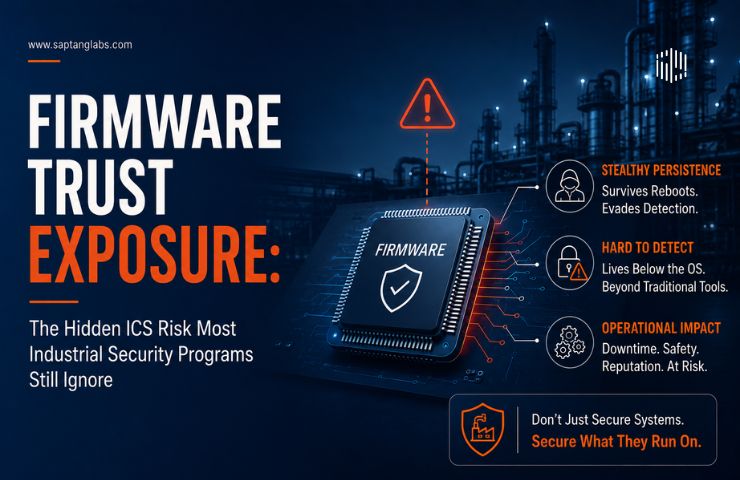
Firmware Trust Exposure: The Hidden ICS Risk Most Industrial Security Programs Still Ignore 

Firmware Trust Exposure: The Hidden ICS Risk Most Industrial Security Programs Still Ignore  TL;DR The foundation of industrial control systems relies heavily on an assumption that the underlying hardware components operate exactly as the manufacturer intended. This assumption creates a massive vulnerability known as Firmware Trust Exposure, which occurs when programmable logic controllers and remote terminal units

The Great Internet Heist: Why BGP Hijacking is the Ultimate Infrastructure Invisible Man

The Great Internet Heist: Why BGP Hijacking is the Ultimate Infrastructure Invisible Man TL;DR Border Gateway Protocol (BGP) is the “postal service” of the internet, but it lacks a built-in verification system. BGP Hijacking occurs when a malicious actor falsely claims ownership of a network’s IP address space, effectively “rerouting the mail” to their own