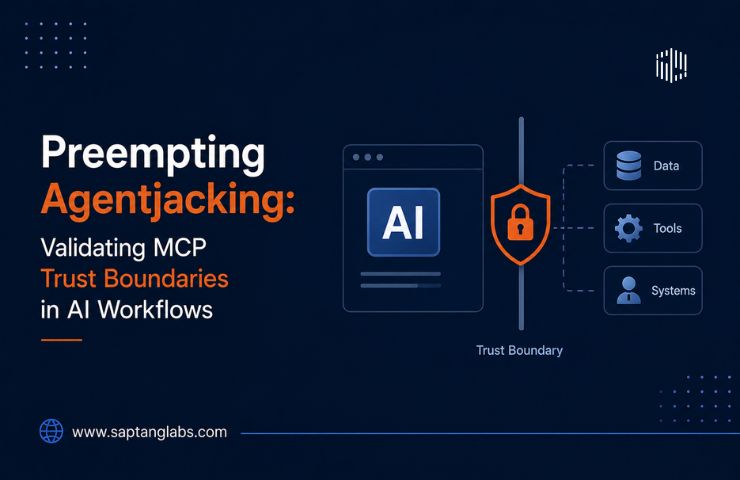
Preempting Agentjacking: Validating MCP Trust Boundaries in AI Workflows

Preempting Agentjacking: Validating MCP Trust Boundaries in AI Workflows  TL;TR In mid June 2026, researchers exposed a devastating new vulnerability class named Agentjacking, which targets autonomous development tools. By abusing the open ingestion architecture of platforms like Sentry and the implicit trust of the Model Context Protocol, attackers can inject malicious markdown into error reports. When an artificial intelligence
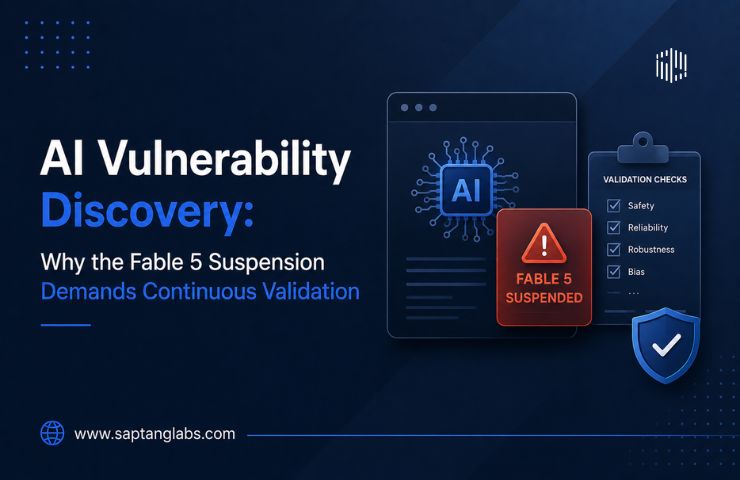
AI Vulnerability Discovery: Why the Fable 5 Suspension Demands Continuous Validation 

AI Vulnerability Discovery: Why the Fable 5 Suspension Demands Continuous Validation  TL;DR The sudden U.S. government directive on June 12, 2026, ordering Anthropic to suspend global access to its advanced Fable 5 and Mythos 5 models, marks a historic inflection point in enterprise security. The core issue driving this national security concern is AI Vulnerability Discovery.

Architecting the AI-Enabled Vulnerability Analysis Loop: Lessons from Anthropic and DevSecOps 

Architecting the AI-Enabled Vulnerability Analysis Loop: Lessons from Anthropic and DevSecOps  TL;TR  The transition from static rule engines to an active AI-Enabled Vulnerability Analysis loop marks the most significant evolution in DevSecOps in a decade. Recent guidance from Anthropic and methodologies taught in advanced security courses like SANS SEC543 highlight a crucial reality. Discovering flaws with Large Language Models is

The Invisible Inventory: Why Shadow APIs Are the Single Point of Failure for 2026 Enterprises 

The Invisible Inventory: Why Shadow APIs Are the Single Point of Failure for 2026 Enterprises Shadow APIs represent undocumented endpoints in production environments that handle real traffic but escape security oversight. These hidden interfaces, often created during rapid development cycles or through third-party integrations, create massive blind spots for enterprises. In 2026, they account for a significant portion of